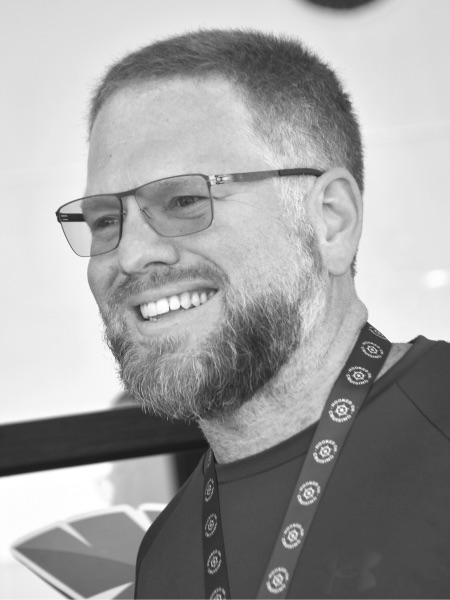
I’m a security researcher and application security engineer. I hunt vulnerability patterns — especially in web apps and cloud services — and I build the tools and references I wish I’d had on the engagement. I founded the OWASP Indianapolis Chapter in 2005 and I still run it; it’s grown to 500+ members. I also curate appsec.fyi, a library of 9,000+ application security resources.
I’m a Senior Security Researcher on the Azure DevSec team at Microsoft, focused on variant hunting, lately around SSRF and related web bugs. Before that I did product security at Proofpoint, Salesforce, Teradata, and Anthem. On my own time I do memory-safety research in C/C++ media software: a use-after-free I found and patched shipped in Kodi v22, and I have a Found-by credit in an upstream FFmpeg fix. I’ve spoken at DerbyCon and CircleCityCon, and I write the guides and research notes on this site.
Selected work
Research
- Kodi use-after-freeFound and patched it; shipped in Kodi v22
- FFmpeg uninitialized memoryFound-by credit in the upstream fix
Tools
- csp-toolkitCSP analysis and bypass finder, on PyPI
- OutOfBitsOAST with programmable callback responses
- JWT, deserialization and SSRF labsBreak things in the browser
Speaking
- Extending Burp SuiteDerbyCon 2017
- Ruby and SecurityCircleCityCon 2015
Writing
- Bug bounty methodologyMy recon-to-report workflow
- IDORBroken object access, with a testing checklist
- AuthenticationSSO, MFA, passkeys and the bypasses
- Leaked secretsDorks for API keys and tokens
- Security conferences 2027Dates, open CFPs and who's speaking
📝 Latest post
An AI Agent Deleted a Production Database. Here's How to Stop Yours.
Least privilege for AI agents: an AI agent deleted a production database in 9 seconds. How to scope coding agent permissions, with a checklist.
Recent Posts
WebAssembly security: what the sandbox actually gives you (and what it doesn't)
Every few months someone tells me WebAssembly is “sandboxed and memory-safe,” usually as a reason they …
Hand-rolling an LDAP listener to catch Log4Shell callbacks
Fifth in a series on building OAST infrastructure from scratch. Post 1 built the javax.naming.Reference that an LDAP …
Fail the build when your CSP regresses
CSP policies regress silently. That’s the whole problem. Someone adds 'unsafe-inline' to script-src to unblock a …
Multi-tenant isolation as defense-in-depth: when WHERE owner_user_id isn't enough
Fourth in a series on building out-of-band application security testing (OAST) infrastructure from scratch. Earlier …
Six layers to sandbox untrusted Python — and the escape I missed
Third in a series on building out-of-band application security testing (OAST) infrastructure from scratch. Post 1 …